Powered by Blogger.
Showing posts with label News. Show all posts

Microsoft Kept Secret That It Suffered a Data Breach Four and a Half Years Ago


Reportedly, Microsoft had suffered a data breach in 2013 when a highly-skilled hacking group by various names including Morpho, Butterfly and Wile Neutron, who exploited a Java Zero-Day vulnerability to hack into Apple Mac computers of the Microsoft employees.

When Microsoft discovered the compromised database in earlier 2013, an alarm spread inside the company. With such a database in hands, the so-called highly sophisticated hacking group could have developed zero-day exploits and other hacking tools to target systems worldwide.

There's no better example than WannaCry ransomware attack to explain what a single zero-day vulnerability can do.

Following the concerns that hackers were using stolen vulnerabilities to conduct new attacks, the tech giant conducted a study to compare the timing of breaches with when the bugs had entered the database and when they were patched.

On being contacted, Microsoft declined to speak about the incident, beyond saying: "Our security teams actively monitor cyber threats to help us prioritize and take appropriate action to keep customers protected."

via: TheHackerNews

Facebook: AEPD Fine $1.43 Million for Violating Users' Privacy in Spain


Social media giant Facebook once again fined by Spanish Data Protection Agency (AEPD). AEPD has issued a €1.2 Million (nearly $1.4 Million) fine against Facebook for breaching laws designed to protect its people's information and confidentiality.

Recently, Tech giant Google was also fine of $2.7 billion (€2.42 billion) by the European antitrust officials on manipulating search results since at least 2008.

The AEPD found Facebook collecting sensitive data on user's ideology, sex, personal tastes, religious beliefs and navigation, either directly from its own services or through third parties without clearly informing it's users how this information would be used.


The AEPD also identified two serious violation of privacy laws, following are:
  1. Tracking people through the use of "Like" button social plug-ins embedded in other non-Facebook web pages—for which it is fined €300,000 ($359,049).
  2. Failing to delete data collected from users once it has finished using it, in fact, the company "retains and reuses it later associated with the same user"—which resulted in another €300,000 ($359,049) fines. 


However, Tech giant Facebook denied any wrong doing and intended to appeal the decision of the AEPD providing the following statement. 

"We take note of the DPA's decision with which we respectfully disagree. Whilst we value the opportunities we've had to engage with the DPA to reinforce how seriously we take the privacy of people who use Facebook, we intend to appeal this decision." 
"As we made clear to the DPA, users choose which information they want to add to their profile and share with others, such as their religion. However, we do not use this information to target adverts to people."
In May, the social media giant was fined €150,000 ($179,532) by for the way Facebook targeted advertising and tracked users.

Google Chrome Warn Users of ‘Man in the Middle’ Attack

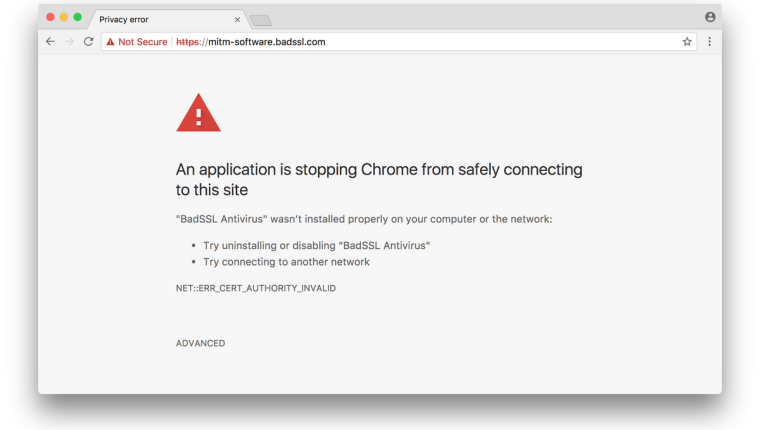
Tech giant Google finally rolling a new security feature for it's users in it's most used product Chrome Web browser and taking security measures seriously.

Google announced that it's upcoming chrome 63 browser will be equipped with new security feature that will alert users of 'man in the middle' attacks aka MITM in which the hacker intercepts communication between two systems.

The developer behind this technology is Sasha Perigo who announced the news on her twitter account.
“Excited to announce my intern project is launching in @GoogleChrome M63! New error pages to help users struggling with MITM software,”

Pakistan & India Hit by State-sponsored Cyber Espionage Campaign


Symantec: A security firm has discovered another espionage campaign against Pakistan & Indian likely to be state-sponsored. Symantec security experts have uncovered a sustained cyber champaign against Pakistan and Indian entities involved in regional security issues.


The nature of the targets and the threat actors' techniques suggest it is a state sponsored campaign likely powered by several groups of hackers.

Uk Government Is Recruiting Security Professionals to Crackdown Criminal Communities Operating in Dark Web Marketplaces.


The United Kingdom National Crime Agency (NCA) is recruiting cybersecurity experts and dark web analyst to track down criminals involved in illegal activities and break down drug rings operating in dark web marketplaces.

National Crime Agency aims to improve his abilities to investigate illicit activities in dark web market, the NCA was searching for G5 Armed Surveillance Investigator in the Armed Operations Unit, working for the Intelligence and Operations Directorate. It offered a salary of £33,850.


Cyber security experts and dark web analysts could help the NCA to contrast illegal activities involving drugs, weapon distribution, and money laundering, they can also support law enforcement in investigations on people smuggling and sexual abuse of children.

Another crucial aspect for the NCA is the collaboration with other law enforcement agencies and the information sharing.

Recently the US law enforcement’s successfully shut down some of the world’s biggest black marketplaces such as AlphaBay and Hansa.

Russian Lawmaker’ Son Pleads Guilty & Sentenced to 27 Years in Jail on $50 Million Scam


Roman Valerevich Seleznev, also known by his hacker handle Track2, is a Russian computer hacker. He was indicted in Washington in 2011, and has been convicted of hacking into servers to steal credit card data.

Seleznev's activities have been speculated to have caused damages to banks and credit-card companies ranging in the millions of dollars. Seleznev was arrested on July 5, 2014 and was sentenced to 27 years in prison for counts of wire fraud, intentional damage to a protected computer, and identity theft.
Image result for Roman Valerevich Seleznev


Seleznev's 2014 arrest caused controversy as he was arrested outside of the United States, in Maldives, and transported to Guam to stand trial. Citing "law enforcement reasons" the Justice Department would not disclose the location of Seleznev's arrest.
Related image
U.S. Secret Service agents took this photo of Roman Seleznev and an unnamed girlfriend just before his arrest in the Maldives on July 7, 2014. (Courtesy of U.S. Attorney)
Jeh Johnson, Secretary of Homeland Security, said in a statement that the arrest showed that "despite the increasingly borderless nature of transitional organized crime, the long arm of justice - and the Department of Homeland Security - will continue to disrupt and dismantle sophisticated criminal organizations".

Member of "Crackas With Attitude" Jailed for 5 Years for Hacking US Intel Officials

A member of the notorious hacker group "Crackas With Attitude" Justin G. Liverman aka "D3F4ULT", 25 of Morehead City has claimed of being gulity on January 6, Liverman admitted to being the member of conspiracy that called itself "Crackas With Attitude" to commit unauthorized computer intrusions, identity theft, and telephone harassment.” reads the press release published by DoJ.


More About Justin aka D3F4ULT:

Justin Gray Liverman (24) was identified and arrested in September 2016 along with Andrew Otto Boggs (22), of North Wilkesboro, N.C.

Boggs went online with the handle “INCURSIO,” and Justin Gray Liverman, of Morehead City, used the handle “D3F4ULT.”
 
The hackers leaked the personal details of 31,000 government agents belonging to nearly 20,000 FBI agents; 9,000 Department of Homeland Security (DHS) officers and some number of DoJ staffers.


Researcher Found Critical Zero-day Vulnerabilities in D-link 850L Wireless Routers


Security researcher has discovered ten zero-day vulnerabilities in D-link 850L wireless routers. D-Link is a Taiwan-based networking equipment manufacturer company which leave users open to cyber attacks.

Security researcher Pierre Kim discovered zero-day vulnerabilities in D-Link DIR 850L wireless routers, last year Kim also reported several flaws in D-Link DWR-932B LTE router but as per him the company ignored the issues.

The following vulnerabilities are:

  1. Lack of proper firmware protection 
  2. Cross-site scripting (XSS) 
  3. Retrieve admin passwords both LAN and WAN 
  4. Weak cloud protocol 
  5. Backdoor Access 
  6. Private keys hardcoded in the firmware 
  7. No authentication check 
  8. Weak files permission and credentials stored in cleartext
  9. Pre-Authentication RCEs 
  10. Denial of Service (DoS)

The following CVE's are:

  • CVE-2016-10177 for #1 
    • (Backdoor accounts)
  • CVE-2016-10178 for #2 
    • (Backdoor)
  • CVE-2016-10179 for #3 
    • (hardcoded WPS PIN)
  • CVE-2016-10180 for #4 
    • (WPS PIN generation based on srand(time(0)) seeding)
  • CVE-2016-10181 for #5 
    • (qmiweb leaks information)
  • CVE-2016-10182 for #6 
    • (qmiweb allows command injection with ` characters)
  • CVE-2016-10183 for #7 
    • (qmiweb allows directory listing with ../ traversal)
  • CVE-2016-10184 for #8 
    • (qmiweb allows file reading with ..%2f traversal)
  • CVE-2016-10185 for #9 
    • (A secure_mode=no line exists in /var/miniupnpd.conf)
  • CVE-2016-10186 for #10 
    • (/var/miniupnpd.conf has no deny rules)
       
You can also read the full report on Kim's website.

U.S Secret Service Agent Who Stole Bitcoins From Silk Road, Pleads Guilty To Money Laundering

U.S Secret Service Agent Who Stole Bitcoins From Silk Road, Pleads Guilty To Money Laundering

Shaun W. Bridges United state former secret service agent who stole hundreds of thousand of the worth of Bitcoin during an investigation into then-largest underground marketplace Silk Road has now pleaded guilty to money laundering.


Ex-fed in Silk Road case pleads guilty to new money laundering charges
At the time of the Silk Road event, the 46-year-old cop Force was donning the hat of a DEA Special Agent, while the 32-year-old Bridges was operating as a Special Agent of the Secret Service.